Unified
Security Management
Built for CISOs.
Inside the platform
See your whole security program, calmly.
Vulnerabilities, governance, compliance, risk and threat intel live in one quiet, connected workspace.
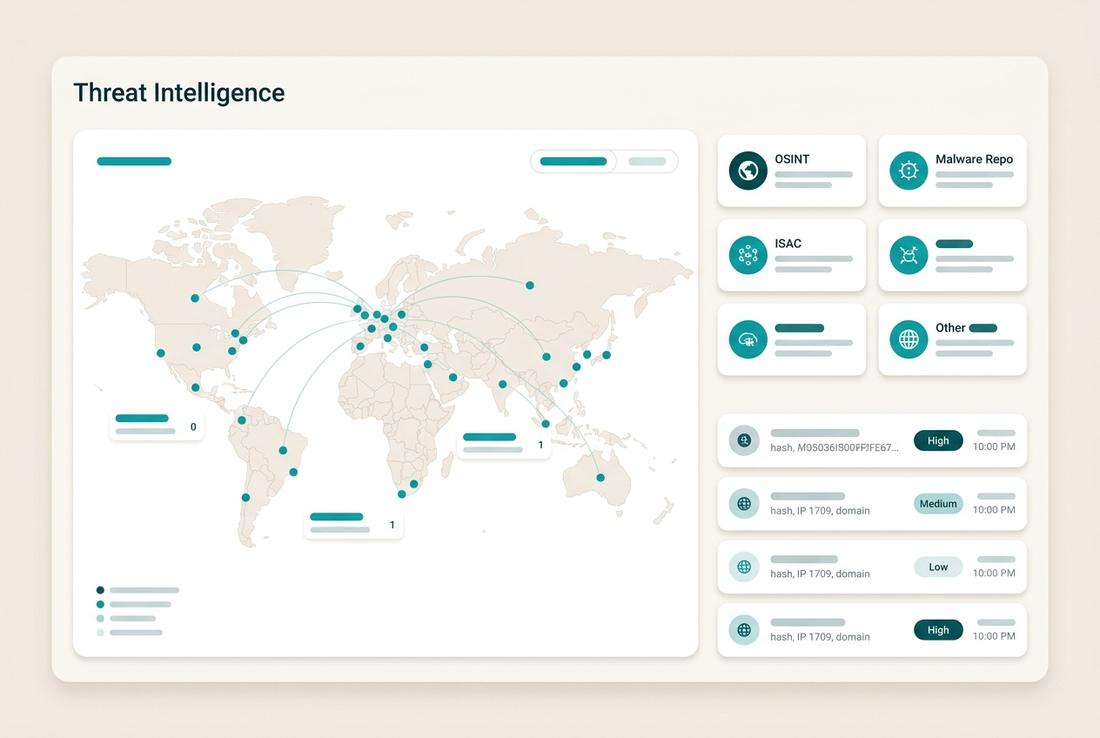
Threat Intelligence
Global threat activity and feed indicators matched against your assets.
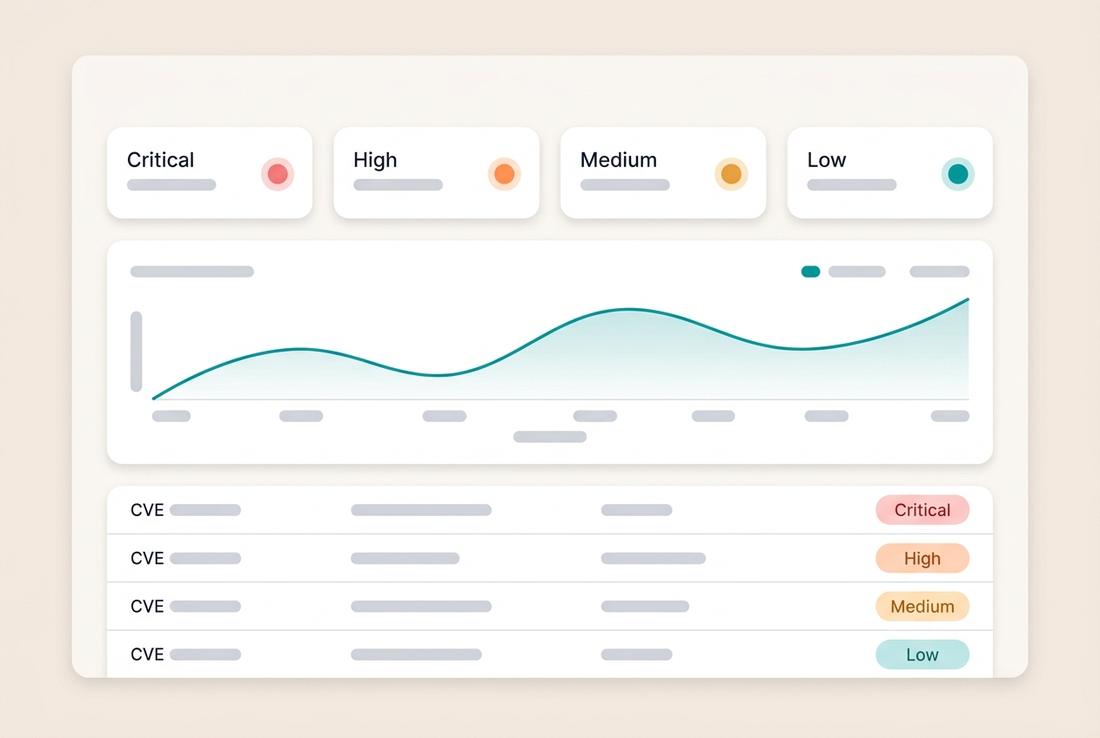
Vulnerabilities
Every CVE ranked by severity, with trends and remediation in one view.
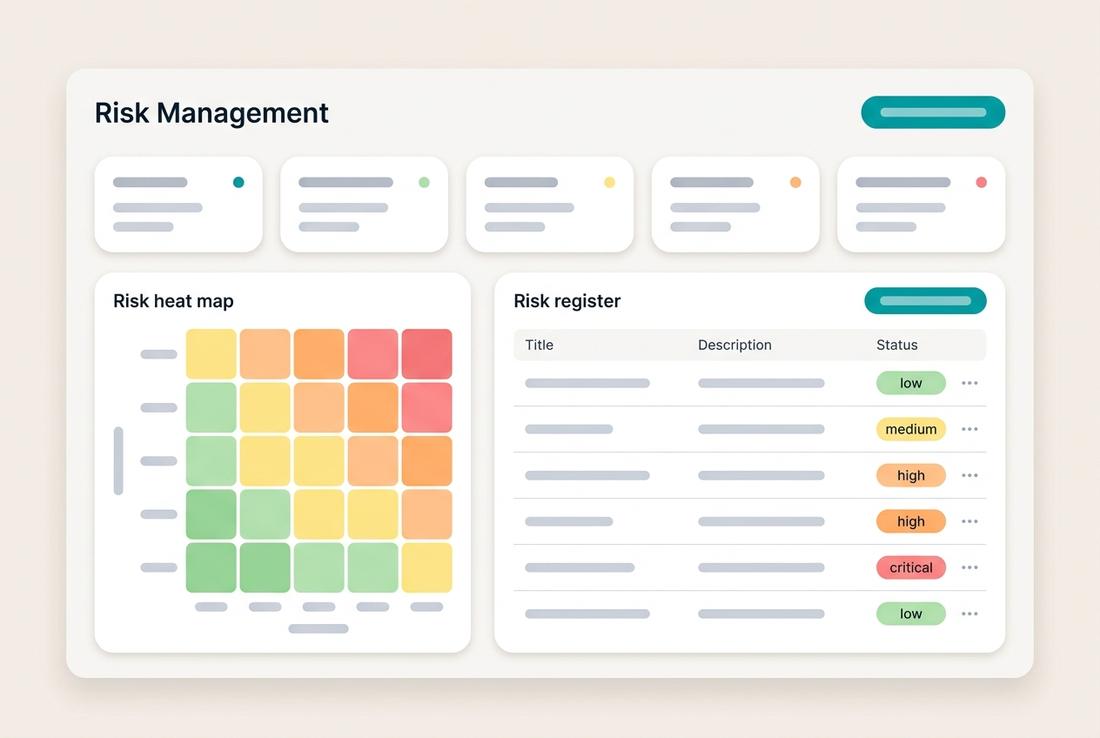
Risk
A live heat map and unified register across vulnerabilities, controls and vendors.
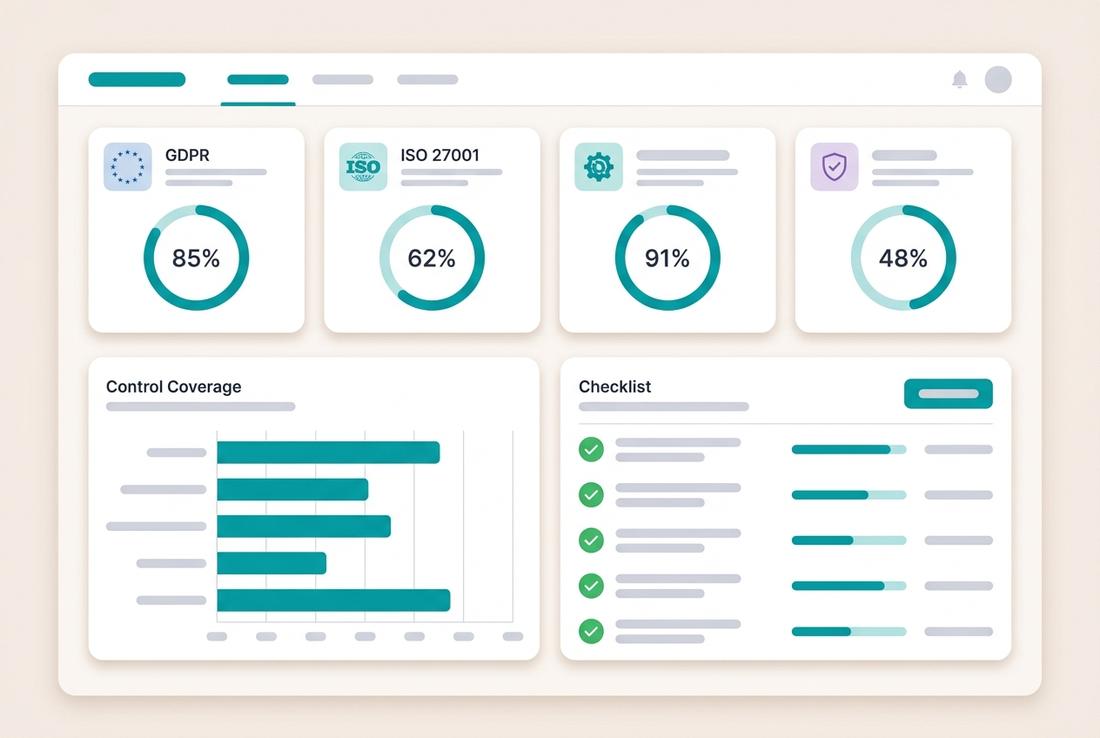
Compliance
Framework readiness, control coverage and evidence tracked side by side.
Governance
A searchable policy library with approvals and review status at a glance.
What CyberSenta does
Six services. One security operating system.
CyberSenta replaces the patchwork of GRC tools, spreadsheets and inboxes with a single platform where governance, risk, compliance, Zero Trust and operations share the same data, approvals and evidence.
 01 · Govern
Govern
Policies, approvals and tickets that actually get signed
Every policy, SOP, risk acceptance, patch and System Security Plan flows through one approval engine with 1- or 2-step workflows, approver groups and a full audit trail.
- Versioned policy library with review & expiry tracking
- Unified ticket queue: attachments, @mentions, threaded notes, reassignment, due-date reminders
- PDF / Excel ticket exports for audit meetings
- Encrypted team messaging with ticket and mention alerts
 02 · Assess
Assess
A live risk register fed by everything you already run
Scanner findings, uploaded results, SIEM alerts, baseline failures, vendor scores and flagged compliance controls all land in one prioritised register — no spreadsheets.
- Control gaps: "Mark as risk" on any framework control, one-click POA&M with owner and milestones
- Formal risk acceptance with expiry, renewal and auto-escalation
- Third-party risk tiering, assessments and reminder nudges
- Board-ready risk posture, trends and executive PDF reports
 03 · Comply
Comply
Frameworks mapped to your systems, evidence included
SOC 2, ISO 27001, NIST 800-53, PCI DSS, CMMC, HIPAA and more — assigned per system, with implementation statements, tools and control owners on every control.
- System Security Plan export per system — branded PDF or Word, sent for CISO sign-off
- Evidence Library with validity dates, control tagging and audit packs
- Configuration-baseline scans that prove technical controls
- Cross-framework comparison so one piece of evidence satisfies many
 04 · Protect
Protect
Zero Trust posture scored from real telemetry
Connect your identity provider and EDR and CyberSenta scores Identity, Devices, Networks, Applications and Data against the CISA maturity model — from evidence, not opinions.
- 8 identity providers: Entra ID, Okta, Google Workspace, JumpCloud, OneLogin, Auth0, PingOne, Keycloak
- 8 EDR platforms: CrowdStrike, Defender, SentinelOne, Cortex XDR, Trend Vision One, Carbon Black, Sophos, Bitdefender
- Threat-intel correlation of IOCs against your assets
- Shadow-IT detection: sensors with no inventory record
 05 · Operate
Operate
From finding to fixed, with the SLA clock visible
Vulnerability management, patch orchestration and POA&M tracking share one pipeline so remediation pace is measurable and defensible.
- Scanner integrations and CSV import with CISO Top-10 categorisation
- Approval-gated patch deployment and patch-SLA compliance
- POA&M board with milestones, overdue alerts and closure approval
- Asset inventory and systems with criticality, owners and baselines
 06 · Enable
Enable
Built for teams — and for the people who run them
Enterprise administration, role-based access, per-section enablement and AI assistance keep the platform tailored to how your organisation works.
- Users, groups and roles; sections switched on per enterprise
- Email alerts for new users, tickets and mentions (no mail server needed)
- AI Advisor and SOP Generator aligned to your frameworks
- In-app tutorials and a first-login welcome tour for every new user
Frameworks
Every major standard, already mapped.
Twenty-plus frameworks ship in the library with control families, evidence slots and system mappings. Add your own from a spreadsheet when you need something bespoke.
 ISO 27001Information security
 NIST CSF 2.0Cyber risk
 SOC 2Trust services
 PCI-DSS v4.0Payments
 GDPRPrivacy
 CIS ControlsSecure baselines
 FedRAMPUS federal cloudNIST 800-53Control catalogueISO 27001Information securityNIST CSF 2.0Cyber riskSOC 2Trust servicesPCI-DSS v4.0PaymentsGDPRPrivacyCIS ControlsSecure baselinesFedRAMPUS federal cloudNIST 800-53Control catalogueISO 42001AI management
 TISAXAutomotive
 Cyber EssentialsUK baseline
 MITRE ATT&CKThreat techniques
 CSA STARCloud assurance
 NIS2EU critical sectors
 NERC CIPEnergy & utilities
 HITRUSTHealth assuranceISO 42001AI managementTISAXAutomotiveCyber EssentialsUK baselineMITRE ATT&CKThreat techniquesCSA STARCloud assuranceNIS2EU critical sectorsNERC CIPEnergy & utilitiesHITRUSTHealth assurance
How it works
CISO-in-a-Box
Security made simple, powered by expertise and AI. Your tailored roadmap in hours.
Connect & scope
Import assets, group them into systems and connect your identity provider, EDR and scanners in minutes.
Map & measure
Assign frameworks per system; CyberSenta scores compliance, Zero Trust and risk from real evidence.
Decide & assign
Flag control gaps as risks, open POA&Ms with owners and milestones, route approvals through tickets.
Prove & report
Export System Security Plans, audit packs and executive reports — signed off through the same workflow.
Platform Capabilities
Everything You Need
A complete suite of security modules working together — not a patchwork of disconnected tools.
Governance
Versioned policies and SOPs with review dates, framework mapping and formal approval before publication.
Risk Management
A live register built from scanners, SIEM, baselines, vendors and flagged controls, with formal risk acceptance.
Compliance
Frameworks per system with implementation statements, tools and owners on every control — plus one-click SSP export.
Zero Trust
CISA-aligned maturity scoring across five pillars, computed from your identity provider and EDR telemetry.
Tickets & Approvals
One queue for every request: attachments, mentions, reassignment, due reminders and PDF/Excel export.
Evidence Library
Audit artefacts tagged to controls and systems, validity tracking and auditor packs in a single export.
Third-Party Risk
Vendor tiering, assessments and risk scores with automated reminders before reviews fall due.
Threat Intelligence
Feeds, IOC correlation against your assets and intel-confirmed vulnerabilities pushed to the register.
Asset Inventory
Assets grouped into systems with criticality, owners, baselines and EDR-driven shadow-IT detection.
Vulnerability Mgmt
Scanner integration, CISO Top-10 categorisation and remediation that opens POA&Ms straight from a finding.
Operations
Scan-to-risk pipeline, approval-gated patch deployment and patch-SLA compliance at a glance.
Remediation (POA&M)
Plans of action with owners, milestones, overdue alerts and approval-verified closure.
Messages
Encrypted chats and channels where ticket, mention and approval alerts arrive and deep-link to the work.
AI Advisor & SOPs
AI-drafted policies, implementation statements, gap analysis and SOPs aligned to your frameworks.
Enterprise Console
Users, groups, roles, approval workflows, connectors, email alerts, sections and in-app tutorials.
What People Say
Trusted by Security Leaders
“Easily the best software of its type we have seen. It covers all areas of a company's cyber structure and is easy to manage.”
ISO Compliance & Audit Specialist
“Board members are very aware of the cyber risks — the system enables me to give them an ongoing snapshot of how we progress through remediation.”
Head of IT, Textile Engineering
“We now know where our gaps are and what needs attention. The platform prioritizes the most important controls to work on and groups them into actionable tasks.”
Head of IT, Power Generation
“From the software to the support, everything has been delightful. It was instrumental to getting our ISO 27001 and ISO 42001 Certification.”
Head of Risk, Telecommunications
Get started
Ready to simplify your security?
Join security leaders who prove their posture every day with CyberSenta — one platform, every framework, zero spreadsheets.